A restaurant menu, a parking meter, a review page, a shipping label. QR codes are everywhere, and you scan them on autopilot, without a second thought. That is exactly what scammers are counting on. Quishing is QR code phishing: a fake code that drops you on a booby-trapped site built to siphon your data or your money.
Before you pay or sign in, check where the code takes you. Here is where the threat actually stands in 2026, how to spot a fake code, whether a QR code can infect your phone, and how a business can protect its customers. Updated in September 2026 with the summer's cases and the latest official warnings.
What quishing is, and whether you should actually worry
Quishing is phishing delivered by QR code. The same con you already know from email, moved onto a square you scan, sitting right next to smishing (by text) and vishing (by phone call). The goal never changes: lure you onto a fake site and lift your login or your card.
France’s public service Cybermalveillance.gouv.fr described quishing as a relatively minor but real threat in August 2026. Microsoft measured a different thing: QR phishing emails detected by its systems rose from 7.6 million in January 2026 to 18.7 million in March (+146%), then fell to 8.3 million in June. In ESET’s first-half figures, about 11% of the phishing emails it detected contained a QR code, averaging 100,000 detections a month and peaking in April.
Those email figures tell us little about how often someone encounters a fake code in the street. In the UK, an investigation by the Bureau of Investigative Journalism put the losses at £3.5 million in a single year, hitting a third of local councils and a dozen hospitals.
The first peer-reviewed review of the subject, 27 studies pooled in the Journal of Cybersecurity and Privacy in August 2026, lands on the same mechanism every time: a place that feels legitimate, a scan done out of habit, and a destination you cannot see.
QR code scams reported in 2026
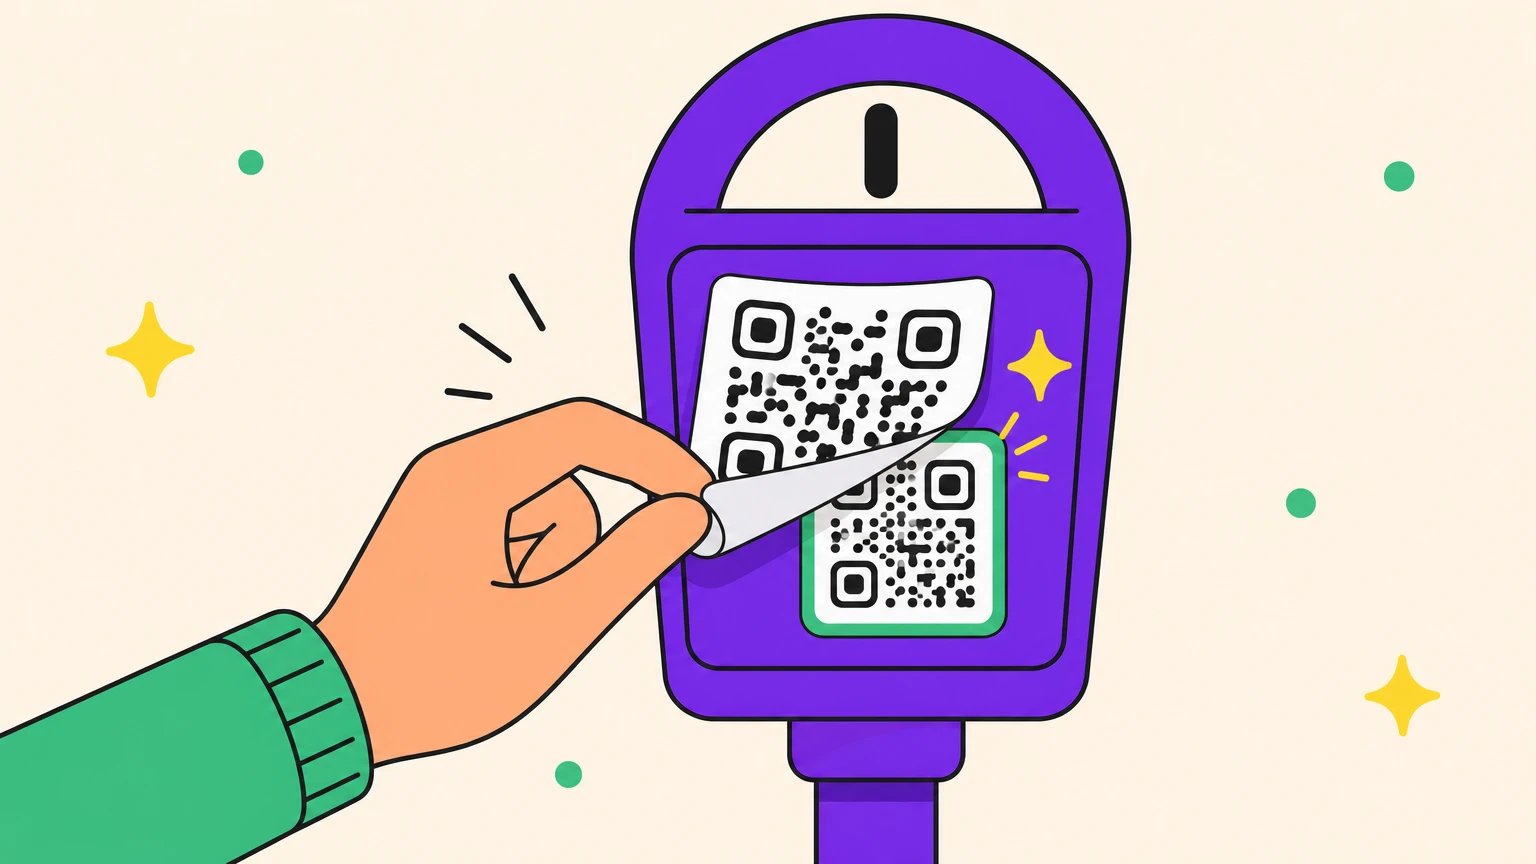
In Toronto, a driver thought she was paying $7 for parking when she scanned the code on the meter. Her bank saw nearly $2,000 go out. Nothing had tipped her off: the payment site looked completely normal.
She is not alone. In one California city alone, police pulled 150 fake codes off parking meters, all pointing to pixel-perfect clones of the official site where only the URL changed. In New York, authorities went as far as telling people to stop scanning meter codes altogether.
This August, on England's north-east coast, a couple scanned the code stuck to the pay-and-display machine of a seafront car park in Whitley Bay. The page carried the RingGo branding down to the privacy policy in the footer. It told them the payment had been declined, so they paid in cash. Overnight, five withdrawals between £20 and £150 left the account, £370 in total. RingGo's response is now a public statement: it never puts QR codes on its parking signs. The scale behind that one story: UK parking QR scams are up 1,300% in three years, with at least £56,000 known to be lost since 2022, and most small thefts never reported.
In 2026, the QR code scam is even moving to the checkout counter. In the US, fake PG&E agents threaten to cut the power, then send a fraudulent QR code for a cashier to scan. The tally: $211,000 gone in the first half of the year.
And in France? A fake "Pay by Phone" code turned up on a parking meter in Paris, along with booby-trapped charging stations out in the Loiret countryside. One creator spent more than four hours hunting before he found a single one in Paris.
The 2026 twist is that the proof itself can be fake. In Nepal at the end of August, a man used ChatGPT to fabricate a payment receipt showing a 120,000-rupee donation to the national flood relief fund, posted it with his own payment QR code, and collected the donations it inspired until Ramechhap police arrested him. The QR code was real. The receipt next to it was generated.
The thread running through all of these: a sticker slapped over something real, or a real code parked next to a fake story.
Why the QR code is a scammer's dream weapon
A QR code is a link your eye cannot read. On a spelled-out web address, you catch the typo or the odd domain name. On a square of pixels, the destination is invisible by design. The whole scam lives in that blind spot.
That blind spot cuts two ways. Out on the street, a sticker laid over a real code goes unnoticed, which is why Toronto police treat it as their most reliable sign of fraud. In your inbox, it slips past filters that read text and links but see the code as just an image. That is why 12% of phishing attacks already hide their trap inside an image.
Some QR readers show the destination before they open it. In our test on an iPhone with Chrome as the default browser, the banner only offered to open in Chrome and named no site. Check the browser’s address bar before you enter any details.
If you cannot confirm the address, open the company’s app or type a web address you already know.
Can a QR code give your phone a virus?
A phone camera can read the data in a QR code, such as a web address, a Wi-Fi password or contact details. Reading an address is different from opening it. A malicious site reached through a QR code can try to steal information or deliver malware, just like a link in a message.
So where does the "virus" come from? From what happens after the scan. Three doors.
The page asks for a login or a card number. That is quishing, most of this article.
A fake page might prompt you to “update your banking app” or “install this viewer to see your parcel”. Canada’s Cyber Centre warns that malicious sites can attempt downloads. Close the page and get any app or update through the official store.
The code triggers an action instead of a page: join a Wi-Fi network, save a contact, send a prefilled SMS, dial a number. Check what your reader proposes before you proceed. And skip third-party scanner apps, a malware risk of their own: both agencies tell you to use the camera that came with your phone.
Keep your phone updated and install apps from the official store.
Spot a fake QR code before you scan it
Start with the sign, then check the address.
Look for signs that someone has covered the original code: a second layer, peeling edges, a crooked sticker or mismatched colours. France’s Interior Ministry recommends checking the surface. If anything looks odd, ask the operator or use another way to pay.
Next, the URL. Read the preview your phone shows before it opens anything. Watch out for shortened links (bit.ly) that hide the destination, and remember the HTTPS padlock proves nothing: a fake site can show one too. Never scan a code that arrives in an unsolicited email or letter, like the phishing scam dressed up as a court summons. If a suspicious page says your payment was declined, stop and check the transaction in your banking app before trying again.
If your password manager doesn’t offer the login you normally use, check the domain before typing it yourself. A QR reader can show the address without opening it. A security checker may recognise a known malicious link, but a clean result cannot establish who runs the site.
A convincing logo is easy to copy. For a payment, use the address or app published by the operator.
Running a business? Protect your posted QR codes (and your customers)
A fake QR code stuck on your counter, and you pay twice: your customer gets their account drained, and your brand takes the blame. You become the backdrop for the scam without ever knowing it.
This is not hypothetical. In Switzerland, a pupil doctored the payment code in a school cafeteria and skimmed off tens of thousands of francs. In the Philippines, a shopkeeper scanned a "customer's" code and watched 80,000 pesos leave the till in four minutes. Small operations are the most exposed: rarely anyone on hand to catch a tampered code.
Here is how to lock yours down:
- Print the domain name in plain text under the code, so customers can compare before they scan.
- Print the code onto the material itself rather than a peel-off sticker, ideally under a tamper-evident cover.
- Build your logo, colours and a frame into the code, to make an unfamiliar replacement easier to spot.
- Train your team to run a regular visual check: extra thickness, misalignment, fading.
- Watch your scan stats, because a sudden drop can be the sign of a hijacked code.
- If your customers pay through an app, say out loud whether you use QR codes at all. Drivers can check RingGo’s published policy before paying.
For a menu or a payment code, tell customers which domain they should expect to see. A password on the code doesn't help either: a sticker laid over yours sends people to someone else's page before any password comes up, one of the limits of a password-protected QR code.
The right reflex takes three seconds
For customers, the most useful check happens before handing over details: open the business’s usual app or type its official address if the payment page looks unfamiliar.
For businesses, a change in the scan count on an Oh My Code QR is a reason to look at the sign. A replacement sticker can send customers straight to someone else’s site, so their scans may never appear in your dashboard.
Your competitors print a black-and-white square and cross their fingers. A sticker can cover both your logo and the QR code, so check the printed code regularly. Create a QR code with your logo.
Frequently asked questions about quishing
What is the FBI warning about QR codes?
Three warnings, in fact. In January 2022, the FBI's Internet Crime Complaint Center warned that criminals tamper with legitimate QR codes to redirect payments and steal logins. In July 2025, it flagged unsolicited packages that arrive with a QR code inside, built to harvest your details or push malware onto your phone. And in April 2026, the FTC added the fake traffic-violation text: a state seal, a case number, and a QR code to "pay the fine". Scan none of them.
What happens if I scan a phishing QR code?
If your camera only showed a link, dismiss the preview. If a suspicious site opened, close it without entering information, accepting permissions or installing anything. If you entered a password, change it on the real site. If you entered card details, contact your bank using a number you trust.
How do I check a QR code before scanning it?
Use a reader that lets you inspect the address before opening it. A short link may conceal the final destination. For a payment or login, use the organisation’s official app or type an address you know. Keep QR codes for tickets or account access out of public online checkers: the code itself can contain a personal link.
What if I already handed over my bank details?
Move fast. Call your bank right away to block the card, then change the passwords on the account and the email address tied to it. Report the scam at reportfraud.ftc.gov if you are in the US, or through your country's national fraud portal, and file a police report: it helps when you dispute the charges.
Is a QR code in an email always a scam?
Not always, but treat it with maximum suspicion. Gmail and Microsoft Defender filters do not catch everything, because a fraudulent QR code shows up as a plain image rather than a readable link. The rule: never scan a code inside an unsolicited email, and type in the address you already know yourself.